What changes for Indian businesses when DPDPA Consent Manager registration opens on 13 November 2026?
November 7, 2026
November 7, 2026
On 13 November 2026, Rule 4 and the First Schedule of the DPDP Rules 2025 come into force, opening registration of Consent Managers with the Data Protection Board. Ordinary data fiduciaries get no new obligation that day. Registration is for Indian companies with ₹2 crore net worth that want to run a consent platform. The duties that bind every business start on 13 May 2027.
The Digital Personal Data Protection Rules, 2025 were notified on 13 November 2025 with a staggered start. Phase one switched on definitions and the Data Protection Board. Phase two arrives next week, on 13 November 2026, and it is the one most often misread. Many CTOs we speak to assume their consent flows must be live by that date. They need not be. This article sets out what actually changes, who it affects, and what a sensible Indian business should do in the six months that follow.
Two things. Section 6(9) of the DPDP Act, 2023, which empowers the government to prescribe how Consent Managers are registered and regulated, and Rule 4 of the DPDP Rules, 2025, read with the First Schedule. Together they open the door for companies to apply to the Data Protection Board for registration as a Consent Manager. Nothing else in the Rules moves on that date; Rules 3 and 5 to 16, which carry the notice, security, breach and rights obligations, remain scheduled for 13 May 2027.
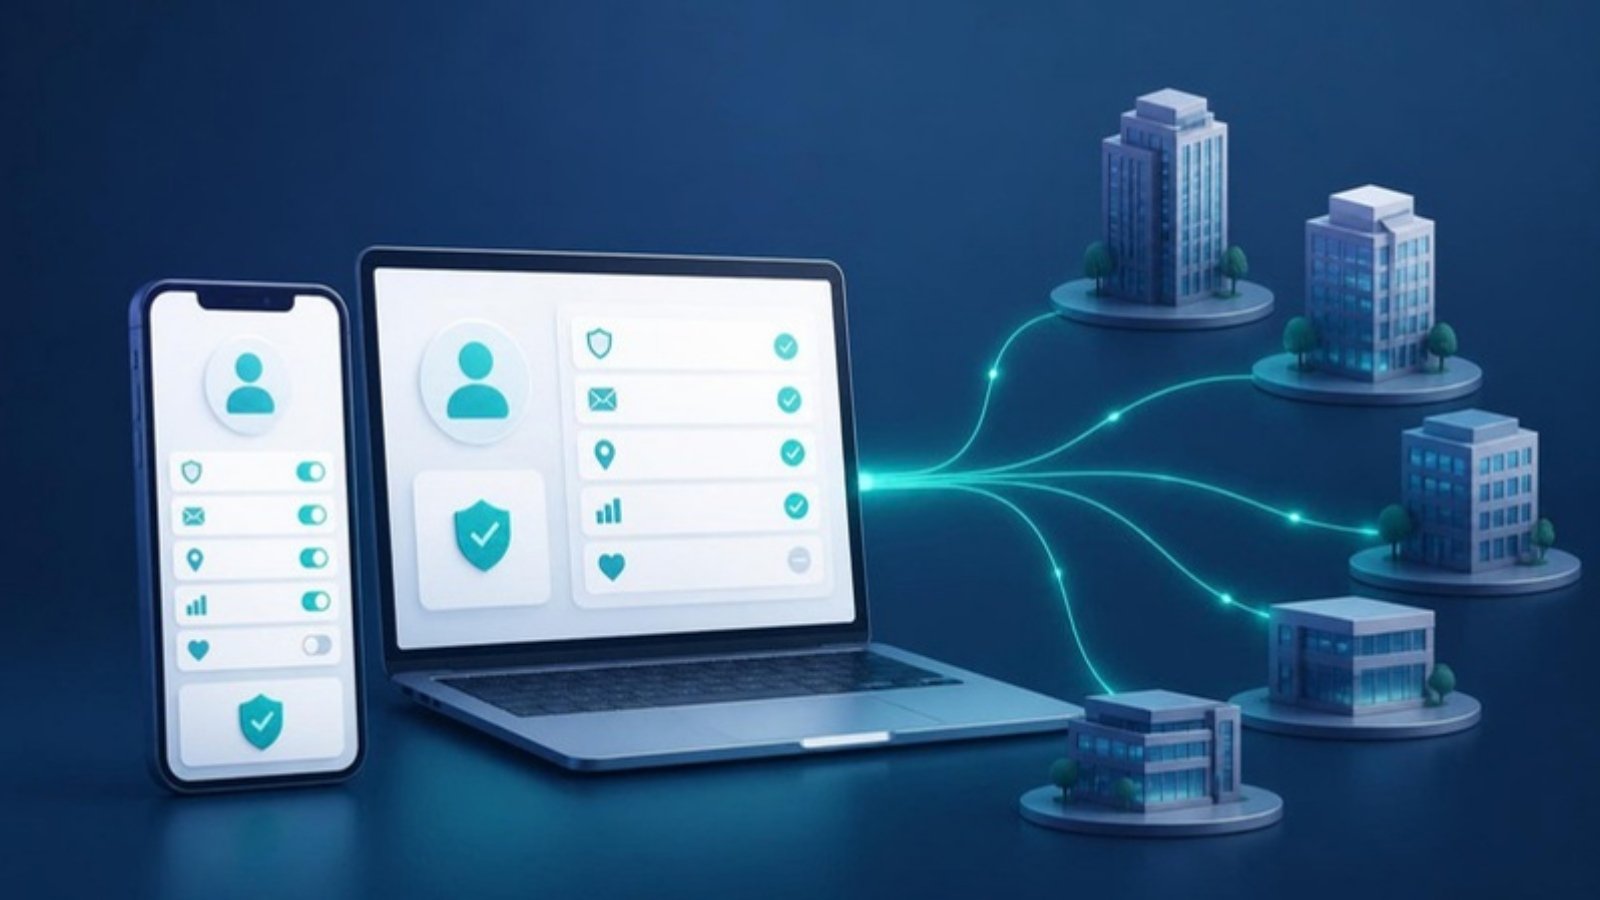
A Consent Manager is a registered intermediary through which an individual can give, manage, review and withdraw consent across many data fiduciaries from one place, in the way Section 6(7) describes. Think of the Account Aggregator model in finance, extended to all personal data: the intermediary carries the consent artefact, never the data itself.
Part A of the First Schedule sets the entry conditions. They are deliberately demanding, because the Consent Manager acts in a fiduciary capacity towards the individuals who use it.
| Condition (First Schedule, Part A) | What it means in practice |
|---|---|
| Company incorporated in India | An LLP, trust or foreign entity cannot apply directly |
| Net worth of not less than ₹2 crore | Total assets minus liabilities as per the books of account |
| Technical, operational and financial capacity | Evidence of a working platform, team and funding runway |
| Reputation of directors and key managerial personnel | A record of fairness and integrity; the Board may inquire |
| Memorandum and articles lock in independence | Conflict-of-interest rules in Part B must be written into the constitution; changes need Board approval |
| Independent certification of the platform | An assessor confirms the interoperable platform meets the Board's published data protection standards |
Rule 4 says the application is made in the form and with the documents the Board publishes on its website. It also lets the Board make any inquiry it considers fit before registering an applicant and publishing its details. In other words, the registration process only starts in practice once the Board has published its application particulars, and public reporting through October 2026 indicates the Board was constituted but not yet operational. Watch the Board's website and the MeitY notifications page rather than relying on the calendar alone.
Part B of the First Schedule lists thirteen continuing obligations. The ones that shape the whole ecosystem are these:
Rule 4 also gives the Board the power to direct a non-compliant Consent Manager, and after a hearing, to suspend or cancel its registration in the interests of data principals. This is a licensed role, not a product category.
Almost certainly not as a registrant. The Act does not require any data fiduciary to route consent through a Consent Manager, and the ₹2 crore net worth and conflict-of-interest rules are designed to keep fiduciaries from registering their own. What the Act does require, from 13 May 2027, is that you can accept consent and withdrawals that arrive through one. Section 6(8) makes the Consent Manager accountable to the individual and able to act on their behalf, so a withdrawal routed through a registered intermediary carries the same weight as one submitted on your own form.
This is where the confusion between a Consent Manager and a consent management platform does real damage. A platform such as DAPro (Data Adhikaar) is tooling that a fiduciary runs to issue notices, capture consent and prove it; a Consent Manager is a third party registered with the Board that individuals use. We explained the distinction in Consent Managers vs consent management platforms. You need the first; you must be able to interoperate with the second.
Six months is enough if the sequence is right. Our recommended order for a mid-size Indian company:
The full phase-by-phase calendar is in our DPDPA compliance timeline. A MeitY proposal from January 2026 to shorten the Significant Data Fiduciary window from 18 to 12 months has not been gazetted at the time of writing, so 13 May 2027 remains the operative date.
Three reasons. First, the day the Board starts accepting Consent Manager applications is the day it is demonstrably functioning, which makes the May 2027 enforcement date credible. Second, the first registered Consent Managers will set the de facto interoperability standard that your consent endpoints must meet; being an early fiduciary partner gives you a say. Third, the penalty schedule is already law: up to ₹250 crore for failing to maintain reasonable security safeguards, ₹200 crore for breach-notification and children's-data failures, and ₹50 crore for residual contraventions. The Board that registers Consent Managers is the same Board that will levy them.
DAPro (Data Adhikaar) is Qodequay's DPDPA compliance platform for data fiduciaries: notices in 22 languages, a tamper-evident Evidence Vault that stores every consent and withdrawal with its notice version, and 25+ connectors to CRM, HRMS and core systems. Qodequay Technologies is ISO 27001:2022 and ISO 9001:2015 certified. If you want a six-month plan to May 2027 mapped to your own systems, book a 30-minute DPDPA readiness call.
No, unless you intend to apply for registration as a Consent Manager. On that date only Rule 4, the First Schedule and Section 6(9) commence. The notice, consent, security safeguard, breach notification, erasure and data principal rights obligations that bind every data fiduciary take effect on 13 May 2027.
Part A of the First Schedule requires a net worth of not less than ₹2 crore, calculated as total assets minus liabilities per the books of account. The applicant must also be a company incorporated in India, show technical and financial capacity, and obtain independent certification of its interoperable consent platform.
No. A consent management platform is software a data fiduciary operates to issue notices and record consent. A Consent Manager is a separate company registered with the Data Protection Board that individuals use to give and withdraw consent across many fiduciaries, and it must remain unable to read the personal data it routes.
In practice, no. Part B of the First Schedule requires the Consent Manager to avoid conflicts of interest with data fiduciaries, including their promoters and key managerial personnel, and to write those safeguards into its memorandum and articles. A captive Consent Manager run by a fiduciary would fail the independence conditions the Board must verify.
At least seven years, or longer where the Consent Manager and data principal agree or the law requires it. The records must cover every consent given, denied or withdrawn, the notices that accompanied each request, and each sharing event with a transferee fiduciary, and must be available to the individual in machine-readable form.
This article is for general information and is not legal advice. Confirm obligations and dates against the official texts of the DPDP Act, 2023 and the DPDP Rules, 2025 as published in the Gazette of India, and consult qualified counsel for your situation.

I am a founder director at Qodequay Technologies Pvt. Ltd., a leading digital transformation consulting firm that helps clients across industries to innovate, optimize, and grow their businesses. I have over two decades of experience in the digital domain, spanning product development, e-commerce, user experience, design thinking, web and app development, and business leadership. My core competencies include developing and executing digital transformation strategies, building teams globally, roadmaps, and solutions that leverage data, insights, and emerging technologies such as artificial intelligence, augmented reality, blockchain, and immersive experience. I also have expertise in digital commerce, supply chain integration, and product management, having worked with both B2B and B2C brands in various sectors. My mission is to create value for customers and stakeholders by delivering impactful and engaging digital experiences that drive growth and innovation.
November 7, 2026
November 6, 2026
November 5, 2026
November 4, 2026
November 3, 2026
Monthly insights on AI, VR and DPDPA compliance — straight from our team to your inbox.
Free 30-minute consultation with our team — or see our products in action.