Can VR count as vocational training for mine workers under India’s 2026 OSHWC Rules?
November 18, 2026
February 13, 2026
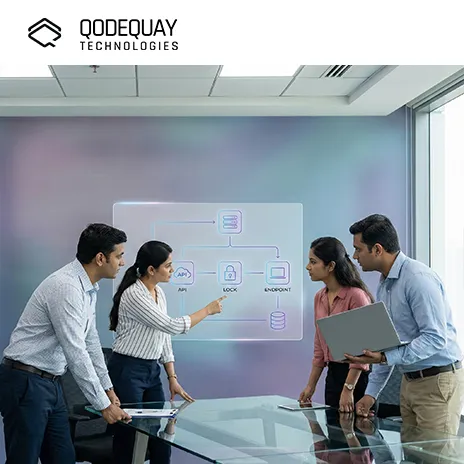
The Secure API Economy is the ecosystem in which organisations expose, consume and monetise APIs while protecting data, identity and service reliability. Because modern products, partner integrations and internal systems all run on APIs, they are both a growth engine and one of the most targeted attack surfaces, so security has to be the foundation rather than an afterthought.
The Secure API Economy is the reality that your business now runs on APIs, and your growth depends on keeping them reliable, governed, and secure. If you are a CTO, CIO, Product Manager, Startup Founder, or Digital Leader, this is not a technical side quest. It is one of the most direct paths to revenue, partnerships, and customer trust.
Because modern digital businesses are not built from monoliths anymore.
They are built from:
And here is the scary part:
APIs are also one of the most targeted attack surfaces in modern security.
So when you talk about the “API economy,” you are really talking about two things at the same time:
In this article, you will learn what a Secure API Economy is, why it matters, how it works, real-world examples, best practices, common failures, and future trends.
The Secure API Economy is the ecosystem where organizations expose, consume, and monetize APIs while protecting data, identity, and service reliability.
An API economy exists when:
Security becomes the foundation, not an afterthought.
A Secure API Economy ensures:
The Secure API Economy matters because APIs directly drive revenue, partnerships, and customer experience.
If your API fails, your product fails.
If your API leaks data, your brand suffers.
If your API is slow, your users blame the product, not the API.
As a leader, you care about:
APIs touch every one of these.
APIs became the backbone because digital products shifted to microservices, mobile apps, and cloud-native architectures.
In the past:
Today:
Examples of API-first businesses:
APIs are no longer plumbing. They are the product.
The biggest threats are authentication failures, authorization gaps, and business logic abuse.
APIs are attacked because they are:
Key API threats include:
This is the most common and dangerous issue.
Example: A user changes an ID in the API request and accesses another customer’s data.
Weak tokens, insecure sessions, or missing MFA for admin APIs.
APIs return more data than needed.
Attackers spam endpoints to scrape data or cause denial-of-service.
SQL injection, command injection, and other classic vulnerabilities still happen in APIs.
Attackers exploit business logic, not just code bugs.
Example: Repeated refund requests, coupon abuse, account takeover.
Old endpoints remain live after teams forget about them.
These are a goldmine for attackers.
API security failures impact revenue, reputation, and regulatory exposure.
A single API breach can cause:
And unlike many security issues, API breaches often expose:
This is why the Secure API Economy is not optional.
A Secure API architecture includes identity, gateway controls, encryption, monitoring, and governance.
Your gateway is your first line of defense.
It provides:
Most secure APIs use:
Authorization ensures a caller can access a specific resource.
Best practice is:
You need:
Secure APIs must be:
You build trust by providing secure onboarding, predictable behavior, and transparent policies.
Partners need:
Security is part of partner experience.
A secure API is a product feature.
Many industries already operate as API economies.
Payment APIs must handle:
A secure API economy is mandatory here.
Open banking depends on APIs that share financial data safely.
Security requirements include:
Marketplace APIs enable:
If APIs are insecure, attackers can:
Telecom APIs manage:
These APIs must be hardened because they are critical infrastructure.
A Secure API Economy requires both technical controls and operational discipline.
Here are proven best practices:
You scale securely by standardizing patterns, automating security, and using governance.
Security fails when:
Scaling safely requires:
The trick is to make secure defaults easy.
Zero Trust strengthens API security by assuming no request is trusted by default.
In a Zero Trust API approach:
This is critical in microservices.
Because in modern architectures, internal services talk to each other constantly. If one service is compromised, it can become a pivot point.
Zero Trust reduces blast radius.
You measure success through reliability, security posture, and partner velocity.
Key metrics include:
The goal is not “zero risk.” The goal is controlled, measurable risk.
The future is AI-driven attacks, automated defense, and stronger regulation.
Here are the trends you should expect:
You will increasingly use AI to:
Attackers will:
This raises the baseline of defense.
More countries will enforce:
Security will move earlier in development:
Identity will become the core of API design, not an add-on.
This includes:
The Secure API Economy will be won by organizations that treat APIs as products and security as design.
The API economy is not coming. It is already here, and your business is already living inside it. The only question is whether you will scale it safely or scale it dangerously.
A Secure API Economy protects your customers, your partners, and your reputation while enabling faster product innovation. It is how you grow without becoming a cautionary tale.
And when you want to build API-driven platforms that are not only secure and scalable but also designed for real human workflows, Qodequay brings the design-first mindset. At Qodequay (https://www.qodequay.com), you start with the human problem, then use technology as the enabler to create secure, usable digital ecosystems that scale with trust.
The biggest threats are authentication failures, authorisation gaps and business logic abuse. Specifically: broken object level authorisation (BOLA), where changing an ID exposes another customer's data; broken authentication; excessive data exposure; rate-limiting failures; injection attacks; API abuse such as repeated refunds or coupon fraud; and shadow APIs, old endpoints that stay live after teams forget them.
It combines an API gateway for authentication enforcement, rate limiting and request validation; strong identity using OAuth 2.0, OpenID Connect, JWT tokens and mutual TLS for service-to-service calls; least-privilege authorisation through RBAC or ABAC; TLS in transit and encryption at rest with secrets management; monitoring with logs, tracing and anomaly detection; and governance covering versioning, documentation, review and safe deprecation.
Zero Trust assumes no request is trusted by default: every call is authenticated, authorised and logged, access is least privilege, and internal APIs are protected like external ones. This matters in microservices, where services talk to each other constantly and a single compromised service can become a pivot point. Zero Trust reduces the blast radius.
By standardising patterns, automating security and applying governance. Security fails when every team builds APIs differently, documentation is missing and releases outpace review. Scaling safely needs reusable API templates, centralised identity and policy enforcement, automated security testing in CI/CD, consistent logging and monitoring, and an API governance council or platform team that makes secure defaults the easy path.
Through reliability, security posture and partner velocity. Security metrics include blocked attacks, time to detect suspicious activity, vulnerabilities per release and API inventory completeness. Reliability metrics cover uptime, latency, error rates and rate-limit effectiveness. Business metrics track partner onboarding time, API adoption, revenue from API-driven channels and customer satisfaction. The goal is controlled, measurable risk, not zero risk.

As the CEO and Founder of Qodequay Technologies, I bring over 20 years of expertise in design thinking, consulting, and digital transformation. Our mission is to merge cutting-edge technologies like AI, Metaverse, AR/VR/MR, and Blockchain with human-centered design, serving global enterprises across the USA, Europe, India, and Australia. I specialize in creating impactful digital solutions, mentoring emerging designers, and leveraging data science to empower underserved communities in rural India. With a credential in Human-Centered Design and extensive experience in guiding product innovation, I’m dedicated to revolutionizing the digital landscape with visionary solutions.
Follow the expert :

November 18, 2026
November 17, 2026
November 13, 2026
November 12, 2026
November 11, 2026
Monthly insights on AI, VR and DPDPA compliance — straight from our team to your inbox.
Free 30-minute consultation with our team — or see our products in action.