Consent Managers vs Consent Management Platforms Under DPDPA: What’s the Difference?
October 2, 2026
October 2, 2026
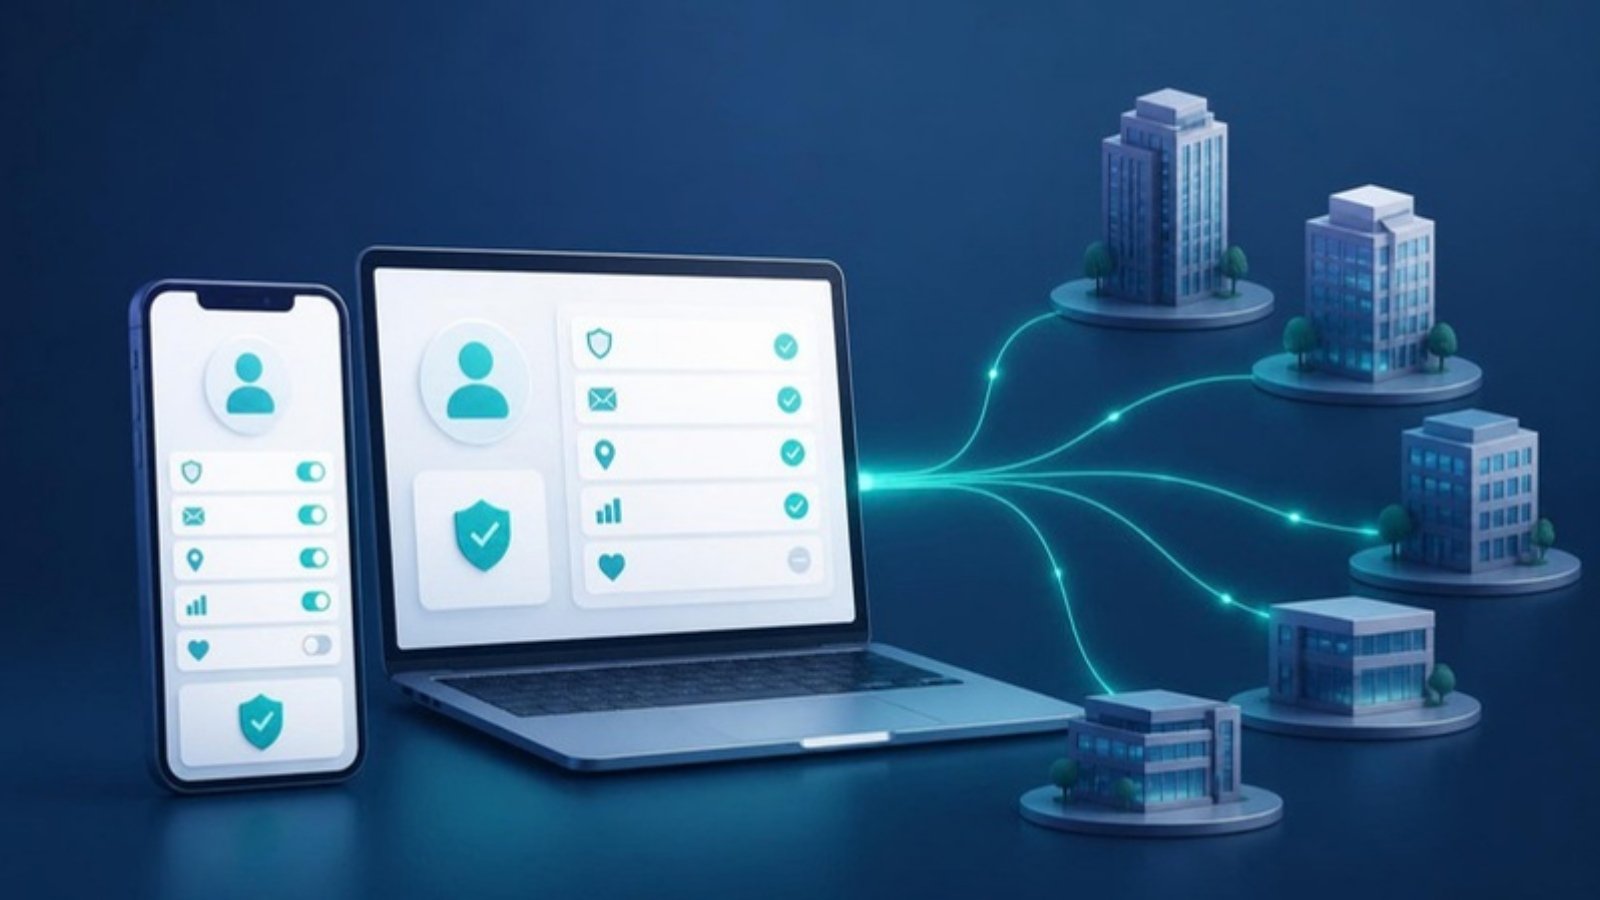
As 13 November 2026 approaches, many compliance teams are hearing that "Consent Managers go live" and wondering whether they need to buy or register something. The confusion comes from two terms that sound alike but mean very different things: a Consent Manager, a regulated entity defined in the DPDP Act, and a consent management platform (CMP), a software tool businesses use to collect and record consent.
Under the DPDP Act, 2023, a Consent Manager is a person registered with the Data Protection Board of India that acts as a single point of contact for Data Principals. Through a Consent Manager's interoperable platform, an individual can give, manage, review and withdraw consent across multiple businesses from one place.
The key point: a Consent Manager works on behalf of the individual, not the business. It is accountable to the Data Principal and must avoid conflicts of interest with the Data Fiduciaries it connects to.
Rule 4 of the DPDP Rules, 2025 sets out who can register. Consent Managers must be companies incorporated in India, meet a minimum net-worth requirement (widely reported as ₹2 crore), and satisfy technical, operational and financial conditions. Rule 4 comes into force on 13 November 2026, one year after the Rules were notified.
A CMP is software your organisation deploys to run its own consent programme: showing notices, capturing consent per purpose, recording proof, handling withdrawal and syncing preferences to downstream systems such as your CRM and marketing tools. It works on behalf of the business, as part of your own compliance obligations as a Data Fiduciary.
| Consent Manager | Consent management platform | |
|---|---|---|
| Legal status | Registered with the Data Protection Board | Commercial software; no registration |
| Acts for | The Data Principal | The Data Fiduciary (your business) |
| Scope | Consent across many businesses | Consent for your organisation only |
| Who needs one | Only entities choosing to operate as Consent Managers | Most businesses processing personal data on the basis of consent |
| Key date | Registration framework live 13 Nov 2026 | Must be operational before core obligations apply (13 May 2027) |
For most businesses, nothing changes directly on that date unless you plan to become a registered Consent Manager yourself. But two things matter:
Treat November 2026 as a readiness checkpoint rather than a finish line. By then you should know where personal data sits, which purposes rely on consent, and how consent records flow between your systems.
If your consent records currently live in spreadsheets or form exports, read why spreadsheets won't survive an inspection.
DAPro (Data Adhikaar) is Qodequay's DPDPA compliance platform for Data Fiduciaries, not a Consent Manager. It helps you run your own consent programme, with notices in 22 languages, a tamper-evident Evidence Vault for consent records, and 25+ connectors to the systems that hold personal data. Book a demo to see how it maps to your data flows.
This article is for general information and is not legal advice. Confirm obligations against the official text of the DPDP Act and Rules and consult qualified counsel for your situation.

I am a founder director at Qodequay Technologies Pvt. Ltd., a leading digital transformation consulting firm that helps clients across industries to innovate, optimize, and grow their businesses. I have over two decades of experience in the digital domain, spanning product development, e-commerce, user experience, design thinking, web and app development, and business leadership. My core competencies include developing and executing digital transformation strategies, building teams globally, roadmaps, and solutions that leverage data, insights, and emerging technologies such as artificial intelligence, augmented reality, blockchain, and immersive experience. I also have expertise in digital commerce, supply chain integration, and product management, having worked with both B2B and B2C brands in various sectors. My mission is to create value for customers and stakeholders by delivering impactful and engaging digital experiences that drive growth and innovation.
October 2, 2026
October 1, 2026
July 2, 2026
July 2, 2026
July 2, 2026
Monthly insights on AI, VR and DPDPA compliance — straight from our team to your inbox.
Free 30-minute consultation with our team — or see our products in action.